AI GxP validation for regulated life sciences
Test Automation

Re-Running a Protocol After a Change: How to Scope Regression Honestly

Automation makes re-running everything cheap, which is exactly why teams stop thinking about what actually needed re-running. Scoping regression on risk rather than on convenience.

Cybroscape Technologies4 min read

Key takeaway

Automation makes re-running everything cheap, which is exactly why teams stop thinking about what actually needed re-running. Scoping regression on risk rather than on convenience.

Automation changes the economics of regression testing, and not entirely for the better. When re-running everything costs an hour instead of a fortnight, the temptation is to stop deciding what needs re-running and simply run it all.

That feels rigorous. It is usually the opposite.

Why running everything is not the safe option

Three reasons, and the third is the one that bites.

  • It hides the reasoning. "We re-ran the full suite" documents an action, not an assessment. An inspector asking why a particular function was re-tested deserves a better answer than "everything was".
  • It produces noise. A full suite on a large system will surface unrelated intermittent failures, each of which now needs investigating, which is how teams learn to wave results through.
  • It stops anyone thinking about what the change touched. This is the real cost. The impact assessment is the control; the test run is evidence that the control was applied. Skipping the assessment because the tests are cheap discards the control and keeps the evidence.

Scoping on what the change can reach

The assessment is not complicated, and it is much the same whether you are automated or not:

  • What changed, precisely — which component, which configuration, which version.
  • What depends on it. Directly, and one step further out. Shared components, integrations, reports that read the same data.
  • Which GxP functions sit in that blast radius, and at what risk classification.
  • Which protocols cover those functions. This mapping is the thing worth investing in — if your protocols are traceable to requirements and requirements to functions, scoping takes minutes.

The output is a named set of protocols, with a sentence of reasoning. That is what goes in the change record, and it is what makes the re-run defensible rather than merely thorough.

Where the cheapness genuinely helps

Having argued against running everything reflexively, there are three cases where low cost changes the right answer.

  • A wide, shallow change — a platform patch, a runtime upgrade — where the blast radius genuinely is everything and the assessment says so.
  • Periodic review. A full run on a schedule, as a check that the system still does what it did, is a good use of cheap execution and a reasonable thing to show at inspection.
  • Before a release you cannot easily roll back. Belt and braces, deliberately chosen and recorded as such.

The distinction is whether the decision was made or defaulted to. Both can end in the same test run; only one of them is a control.

Keeping the mapping current

All of this rests on knowing which protocol covers which function, and that mapping decays quietly. A requirement is reworded, a protocol is revised, a function moves — and six months later the traceability matrix is a document rather than a tool.

Treat it as a live artefact: updated as part of the change, not reconstructed before an audit. See CSA services and GAMP 5 Second Edition consulting for how this fits a risk-based approach, and Cybroscape TraceDraft for keeping traceability attached to the source rather than maintained alongside it.

Where to go next

Explore Cybroscape GxP Copilot for AI-native validation, Cybroscape TraceDraft for source-traceable clinical documentation, or book a demo to see either on your own data.
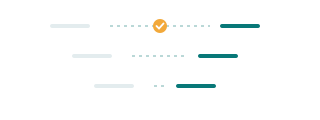
High riskFailure could affect patient safety or product quality
Scripted testingWritten steps, expected results, an independent reviewer
Step-by-step results, screenshots and signatures
Medium riskFailure is noticed and contained
Unscripted testingExploratory or ad-hoc testing against the intended use
A record of what was tested, by whom, and the result
Low riskStandard function, supplier-tested
Supplier evidenceThe vendor’s own testing, assessed and accepted
The assessment and the reason it is enough
Computer Software Assurance in one picture: test effort follows the risk of each requirement. Based on FDA’s Computer Software Assurance guidance.
See it on your own systemBring a URS or a system. We run GxP Copilot against it live on the call.
regression testing gxprevalidation scopechange control testingperiodic review automationimpact assessment validation

Keep reading

All articles
ValidationChange control for computerised systems: the part that keeps validation trueChange control keeps a system validated after go-live. Its core is a real impact assessment: what the change could affect, how you will show it didn’t, and testing proportionate to that risk. · 3 min readAI TransformationGenAI adoption in pharma: from pilot to production without governance driftThe playbook that keeps use-cases moving through the intake without turning into shelfware. · 5 min readBusiness CaseGxP AI Software ROI: A Working Economic Model for Your QA Head and CFOThe real numbers behind GxP AI software adoption: validation cycle time, scripted-test effort delta, re-baseline cost, and the model your CFO will accept. · 4 min readDataOpsGxP Data Integrity Pipeline: Keeping ALCOA+ Intact Across Every System BoundaryHow to build and validate a data integrity pipeline that keeps ALCOA+ evidence unbroken from raw instrument output through regulatory submission. · 5 min readDataOpsGxP DataOps Architecture: Building a Validated Data Pipeline from Instrument to SubmissionThe reference architecture for a GxP DataOps pipeline: ingestion, lineage, integrity checks, transformation, and a compliant serving layer for regulatory submissions. · 5 min readDataOpsLIMS, ELN, MES and ERP Integration in GxP: An Architecture That Holds Under AuditHow LIMS integrates with MES and ERP in a GxP operation, where each handoff breaks, how to validate the interfaces, and how to test end-to-end traceability. · 7 min readDataOpsGxP DataOps Platform Guide 2026: Architecture, Toolchain, and GAMP 5 ValidationThe complete guide to GxP DataOps and regulated data platforms: the 5-layer ALCOA+ architecture, toolchain (Airflow, dbt, Snowflake, LIMS/ELN/MES pipelines), vs traditional data management, and how to validate data pipelines with Cybroscape GxP Copilot. · 7 min readDataOpsGxP DataOps vs Traditional Data Management: What Actually Changes and Why It MattersWhy spreadsheet-and-extract data management fails modern GxP environments, and the operational model that replaces it without sacrificing compliance posture. · 4 min read

Bring a system. We'll show you the package.

Book a demo, or ask a validation lead a quick question on WhatsApp.

  • We reply within one business day
  • We run your URS live on the call
  • You get a clear plan for your system
Chat on WhatsApp

Book a demo

Four fields. The right specialist replies within one business day.

Your details stay private. We never share them.